Diagram showing how a trojanized Atera RMM MSI installer disguised as a bank eStatement establishes persistent remote access via AWS IoT Core MQTT and PubNub channels

Dissecting a Weaponized Atera Installer: How a Fake Bank Statement Grants Full Remote Access

A trojanized Atera RMM installer disguised as a bank eStatement PDF grants attackers persistent remote access including terminal, remote desktop, and arbitrary code execution — all through legitimately signed, commercially trusted infrastructure. Zero public detections at time of analysis. Likely Luna Moth / Silent Ransom Group campaign.

April 7, 2026 · 9 min · 1805 words · Animeh Roy
Diagram illustrating how TeamPCP compromised Trivy security scanner to backdoor LiteLLM Python package via CI/CD pipeline credential theft

How TeamPCP Poisoned Security Scanners to Backdoor LiteLLM

On March 24, 2026, threat actor TeamPCP published backdoored versions of the LiteLLM Python package (3.4M daily downloads) after compromising Trivy and Checkmarx security scanners to steal PyPI credentials from CI/CD pipelines. The malware harvested credentials, deployed Kubernetes worms, and established persistent C2 — all triggered by a Python .pth file that fires on every interpreter startup.

March 26, 2026 · 11 min · 2192 words · Animeh Roy
Annotated screenshot of the phishing staging page showing fake PDF toolbar and redirect mechanism

Quishing in the Wild: Anatomy of a Corporate HR Lure Using QR Codes, AWS S3, and Cloudflare Turnstile

TLP: WHITE — This analysis is cleared for public release. All victim PII has been redacted. No credentials were submitted during analysis. IOCs are provided at the end for detection use. Overview A live QR phishing (“quishing”) campaign was captured in the wild targeting corporate employees via a weaponized PDF disguised as an employee handbook. This isn’t a commodity phish — it’s a toolkit-grade, multi-stage attack built specifically to defeat automated email scanners, security sandboxes, and network proxies. ...

March 11, 2026 · 8 min · 1554 words · Animesh Roy
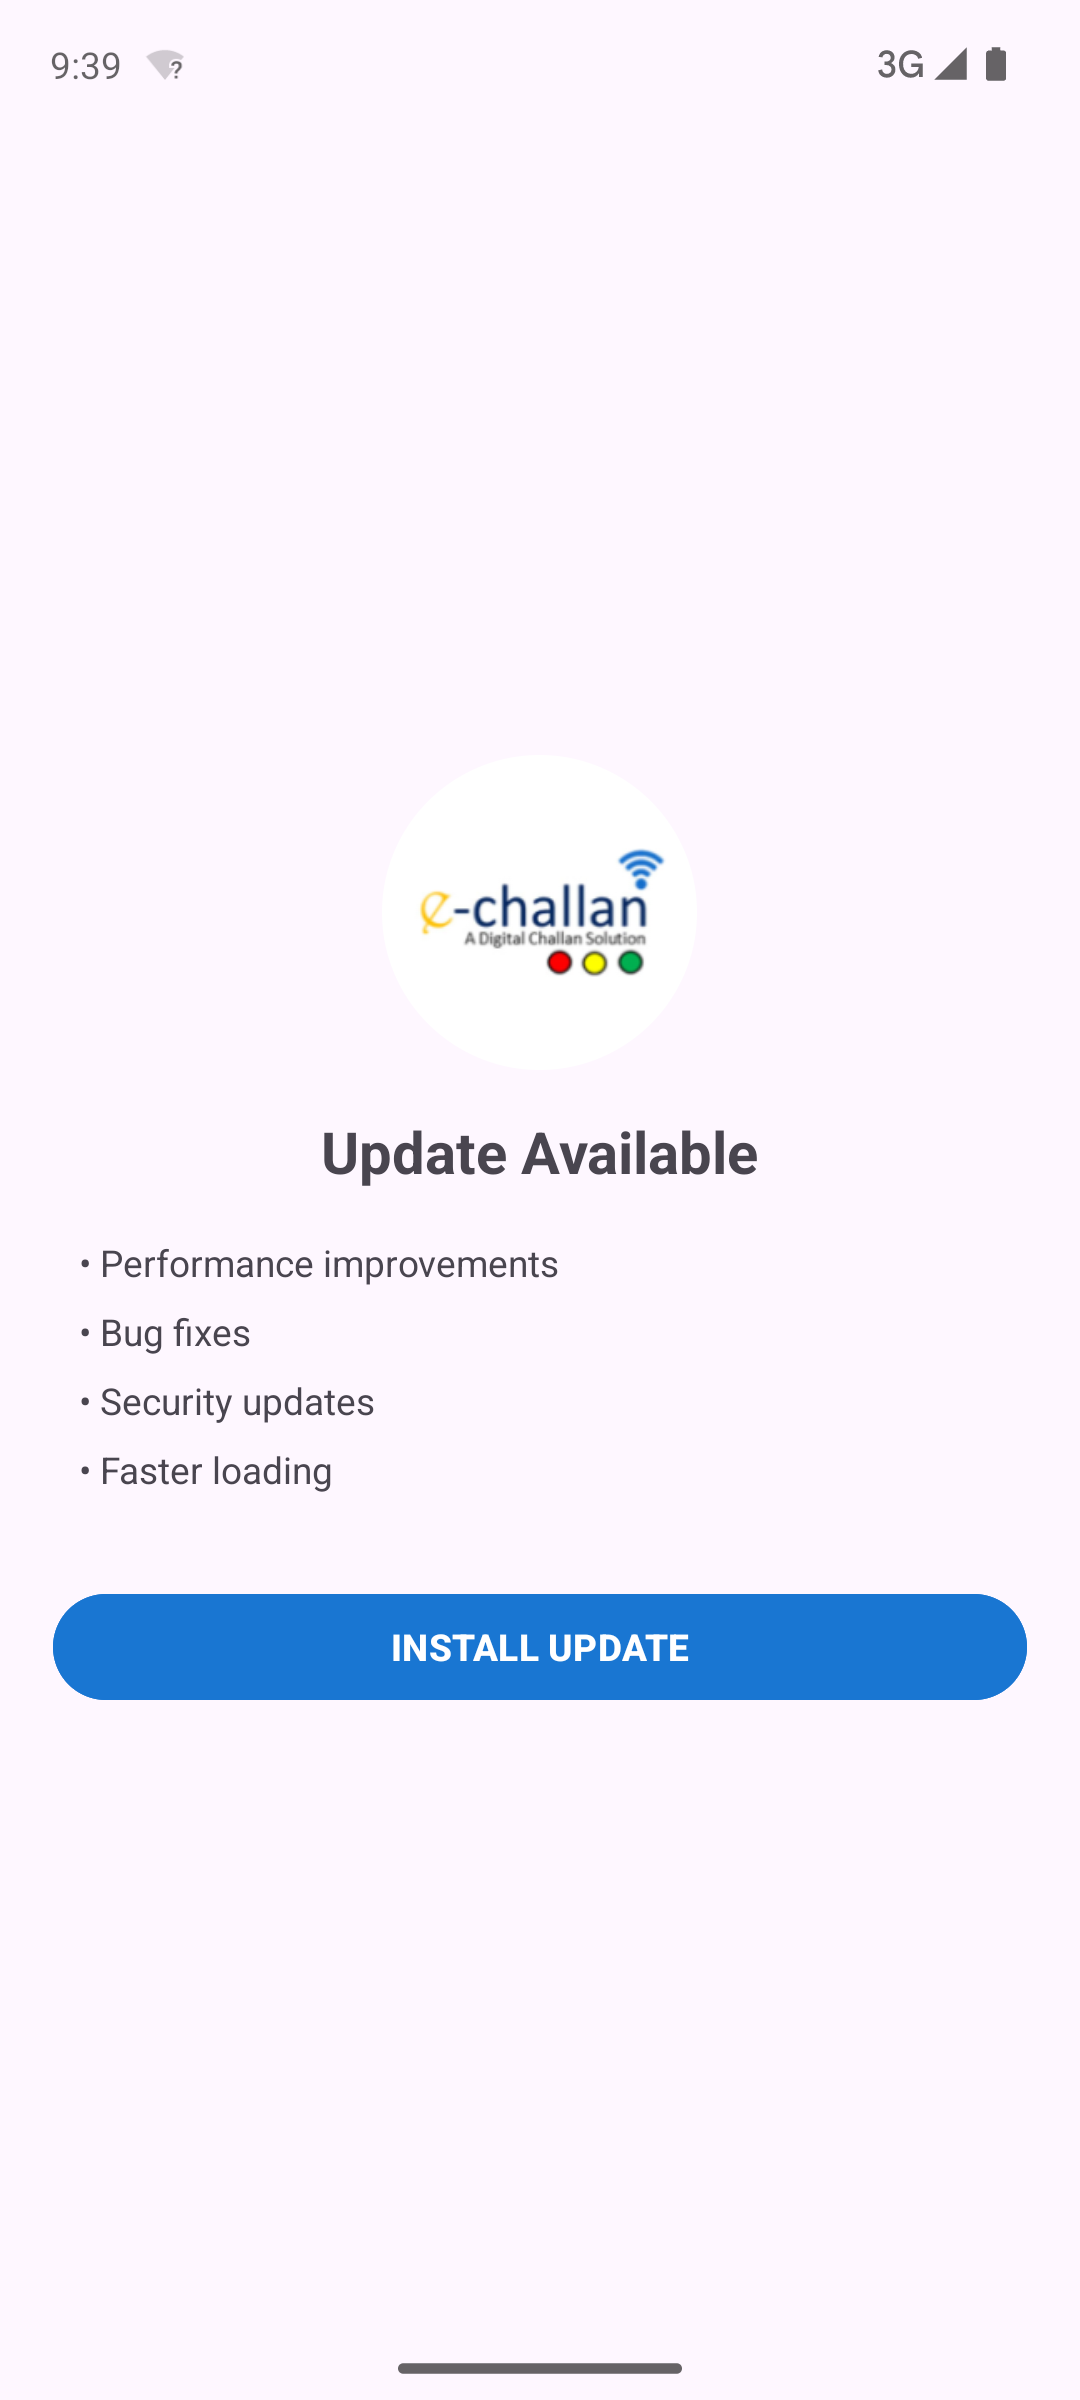
Android banking trojan fake eChallan dropper screen showing fake Update Available prompt

Dissecting a Two-Stage Indian Banking Trojan: From Fake eChallan to Full Device Compromise

A fresh Android malware sample masquerading as an RTO eChallan app. Two-stage dropper with NP Protect packer, SMS interception, USSD banking code execution, Firebase FCM C2, and only 11/66 VirusTotal detections.

February 19, 2026 · 12 min · 2455 words · Animeh Roy
Privacy Policy • Terms of Service