Diagram showing how a trojanized Atera RMM MSI installer disguised as a bank eStatement establishes persistent remote access via AWS IoT Core MQTT and PubNub channels

Dissecting a Weaponized Atera Installer: How a Fake Bank Statement Grants Full Remote Access

A trojanized Atera RMM installer disguised as a bank eStatement PDF grants attackers persistent remote access including terminal, remote desktop, and arbitrary code execution — all through legitimately signed, commercially trusted infrastructure. Zero public detections at time of analysis. Likely Luna Moth / Silent Ransom Group campaign.
April 7, 2026 · 9 min · 1805 words · Animeh Roy
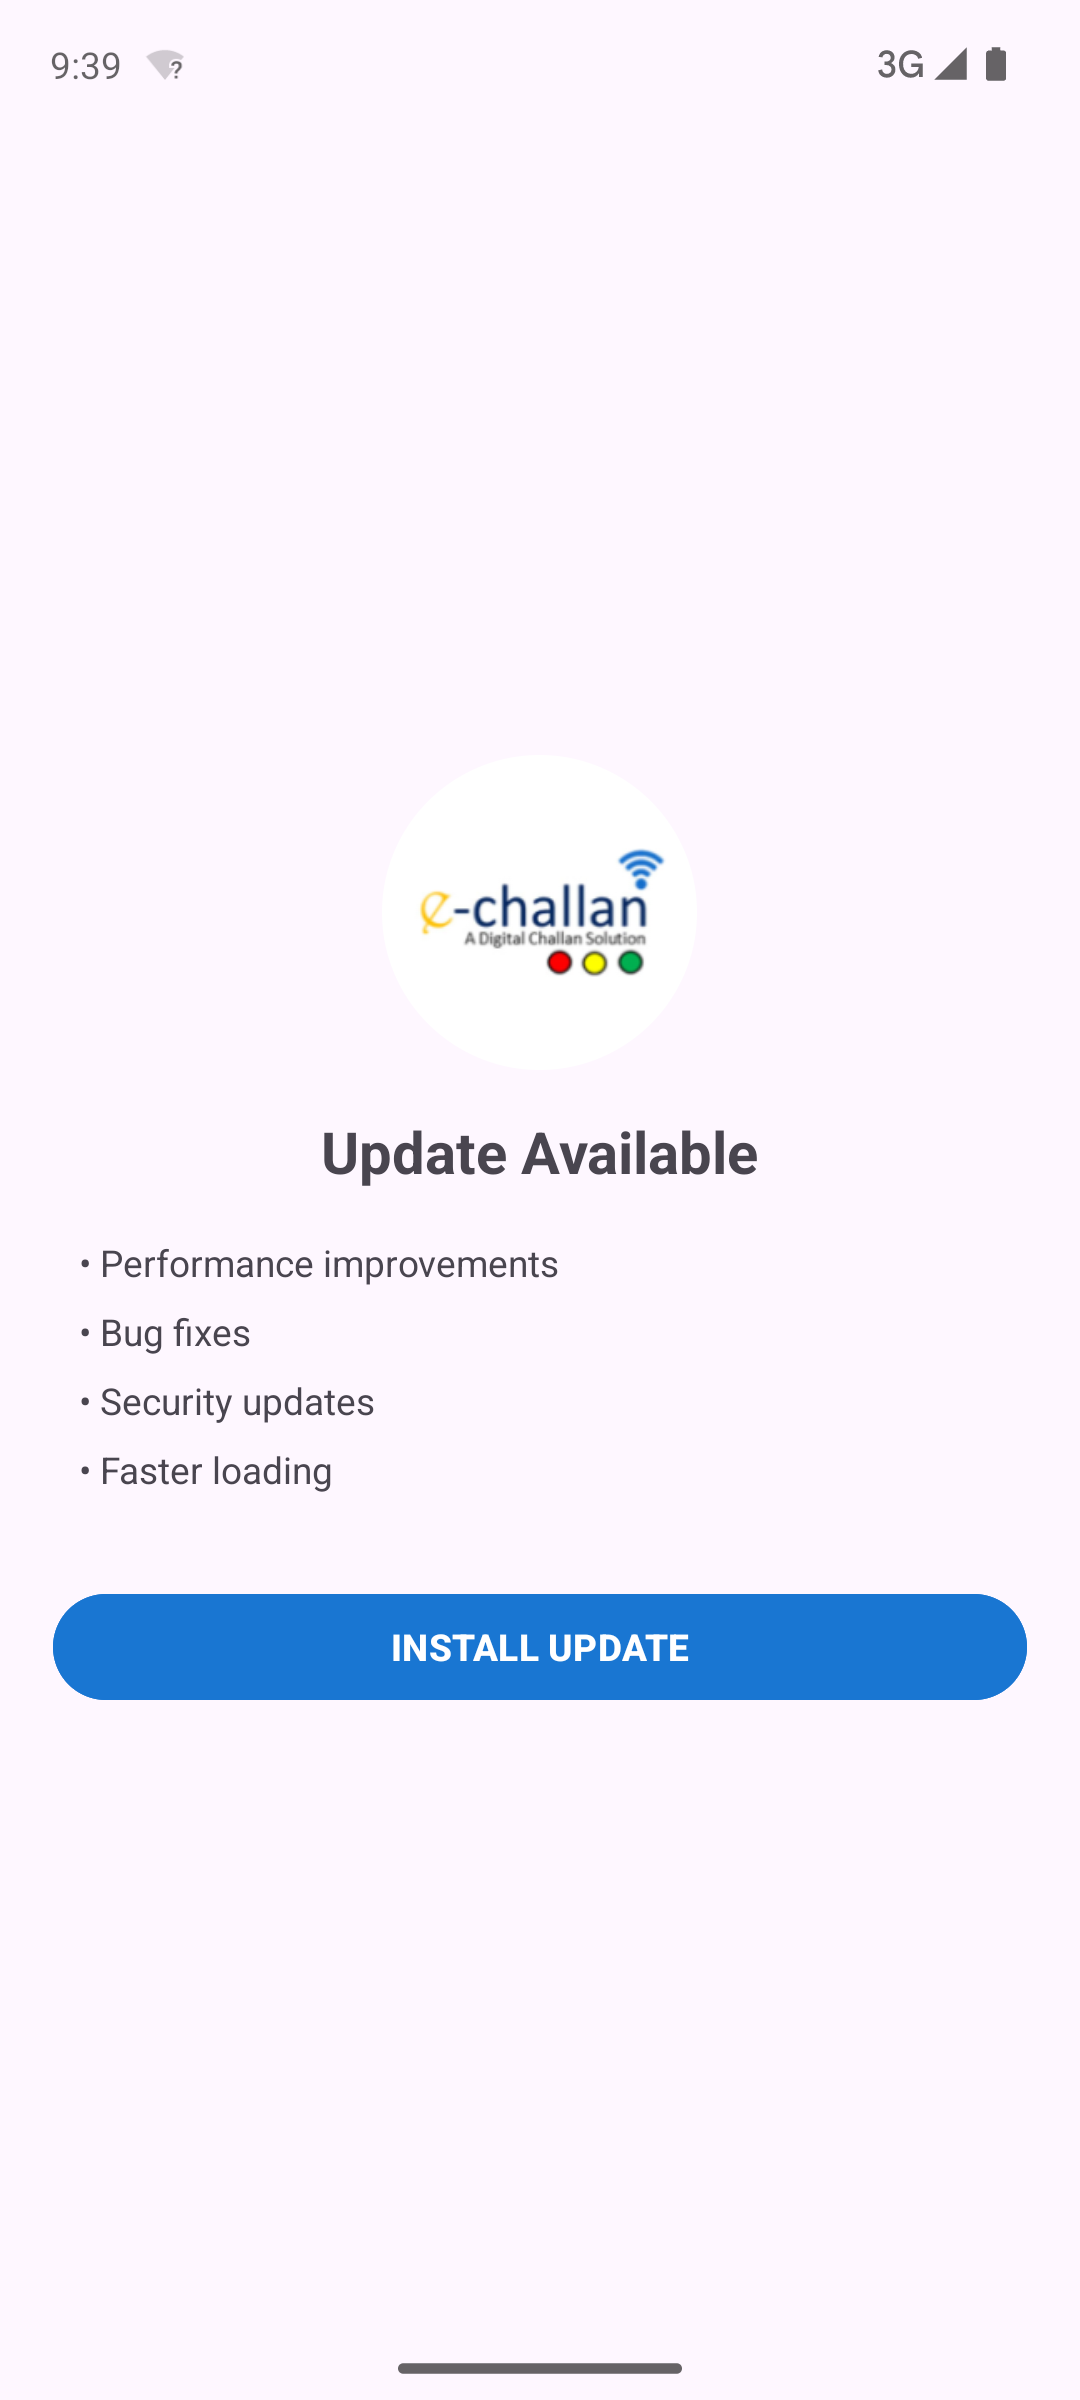
Android banking trojan fake eChallan dropper screen showing fake Update Available prompt

Dissecting a Two-Stage Indian Banking Trojan: From Fake eChallan to Full Device Compromise

A fresh Android malware sample masquerading as an RTO eChallan app. Two-stage dropper with NP Protect packer, SMS interception, USSD banking code execution, Firebase FCM C2, and only 11/66 VirusTotal detections.

February 19, 2026 · 12 min · 2455 words · Animeh Roy
Privacy Policy • Terms of Service